SiteDash feature
MODX security checks and alerts
Compare every site against our MODX and Extras vulnerability data, catch misconfigurations early, and benefit from security-team context when advisories land.
- One month free, full access
- No payment method to start
- Built for MODX agencies
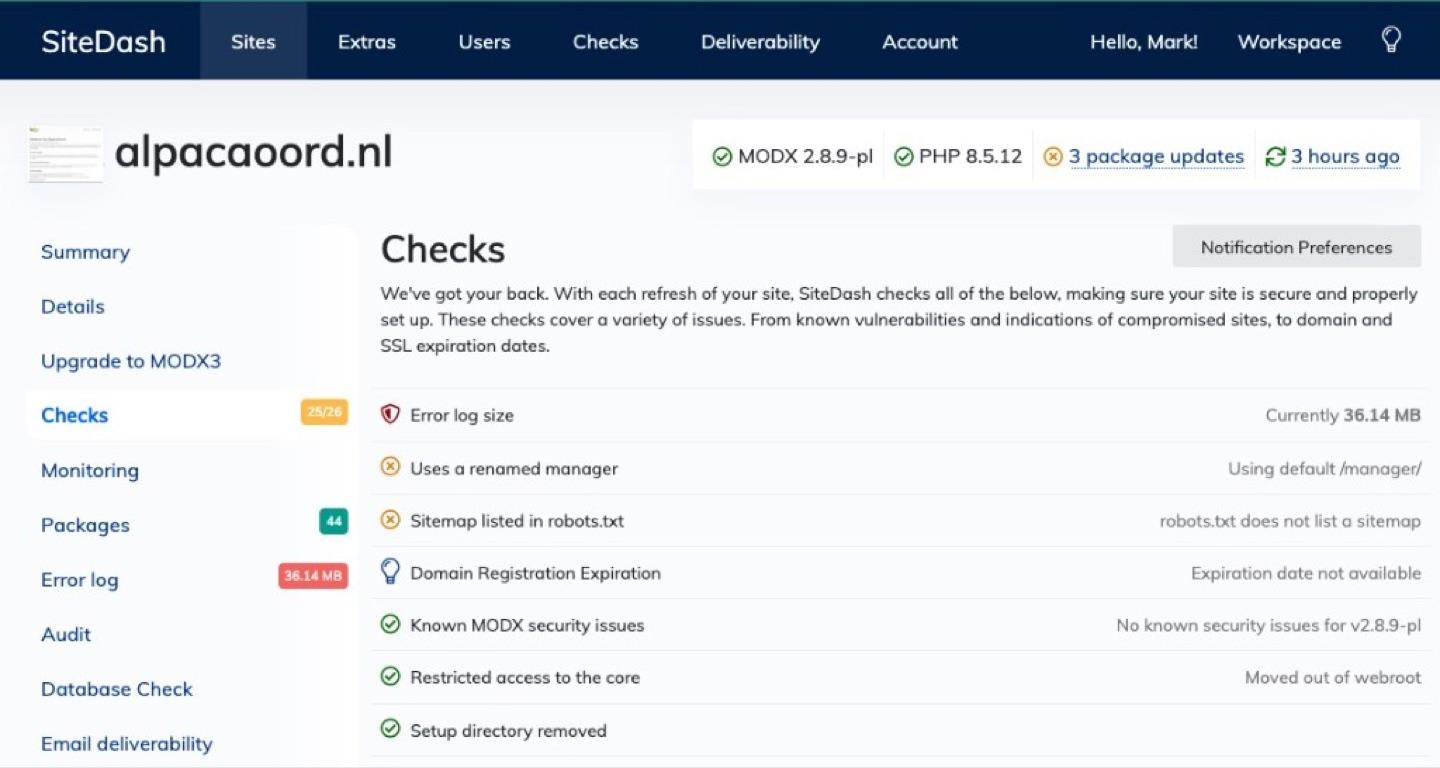
Catch MODX risk early
Security is not a single checkbox. SiteDash runs dozens of checks whenever your site data refreshes, comparing versions against our vulnerability database and inspecting server and MODX configuration that attackers probe first.
When a check fails, you get an Action Center alert and can often remediate from the dashboard with remote upgrades or cache clears. Remote commands are authorized with cryptographic request signing, not shared manager passwords.
Vulnerable MODX versions, leftover setup folder, exposed core directory, renamed manager, and current MODX release tracking.
Known vulnerable package versions, insecure manager usernames, and MODX secure user checks.
PHP version and extensions, php2shell-style risks, TLS/HTTP versions, SSL and domain expiry, disk space, and session table health.
Part of the MODX open source security team
We're part of the MODX core open source security team. We help review reported vulnerabilities, prepare core fixes, and assist with coordinated disclosures behind the scenes.
That perspective helps us give you a leg up: for severe vulnerabilities we can prepare changes before an advisory is public: tuning checks, refreshing vulnerability data, implementing patches to distribute with the Client for an initial response or more. When disclosure happens, we can also immediately inform you: what broke, which sites in your workspace are affected, and practical steps to remediate.
Security does not pause for your sprint planning. This connection is how we help you stay a step ahead in an ecosystem that never stands still.
Automated alerts catch misconfigurations every day. The security team link adds human timing and depth when coordinated releases land, so you are not guessing alone.
Every check in production today
- Known MODX security issues
- Restricted access to the core
- Setup directory removed
- Uses a renamed manager
- Sufficient disk space available
- Error log size
- Supported PHP Version
- PHP php2shell vulnerability
- Required PHP extensions
- Session Table Crashed
- Session Garbage Control
- Domain Registration Expiration
- Expiring SSL Certificate
- Supported SSL/TLS Versions
- Supported HTTP Protocols
- Has accessible robots.txt
- Sitemap listed in robots.txt
- Known vulnerable extras
- Common administrator usernames
- No "modxsecure" user
- SiteDash Client version
- MODX Version in sync
We extend this list as MODX and hosting ecosystems evolve. Public MODX and Extras catalogues feed vulnerability awareness, informed by our participation on the MODX open source security team.
Learn more about: Monitoring · Security · Remote management · Request signing · Action Center · All features
Try SiteDash with a free one-month trial, with all features and no payment method required to get started.